Cyber Security Training
Cyber Security Training
Most entry-level pentesting certifications reward how well you remember a study guide. The Entry-Level Penetration Tester Certification (ELPT) was built to test something harder: whether you can actually run a real engagement from the first scan all the way to a client-ready report.
The course is written and taught by the team at White Knight Labs, a veteran-owned offensive security firm that still does this work for a living. You will spend most of your time inside private cloud labs, working through the same sequence a junior consultant walks through on a real engagement: enumerating the environment, pivoting across networks, attacking Active Directory, dealing with light AV, phishing a user, and documenting everything along the way. When you are ready, you sit a 48-hour performance-based exam that mirrors a short consulting engagement.


ELPT is built to look like the way the industry actually works. You start with foundational material (networking, Linux, Windows, and lab operations) and then move through the same sequence a working pentester would on a real engagement: reconnaissance, enumeration, exploitation, pivoting across internal networks, attacking Active Directory, testing cloud and web applications, running a phishing scenario, and writing it all up in a professional report.
Every module ships with its own private labs, which you launch from the student portal with a single click. The portal takes care of standing the environment up inside your own cloud account, so there are no shared pods to wait on and no queue to sit in. You work at your own pace, on your own schedule.
Real engagements rarely go to plan, so ELPT includes a dedicated When Things Go Wrong module. It walks through the professional-judgement moments every working pentester eventually faces: a production service that crashed under your scanner, a credential lockout at 16:45 on a Friday, a mid-engagement scope expansion request, or evidence that someone else has already compromised the client’s network. Handling those moments well is one of the differences between a junior pentester and one who keeps getting booked.
There is no multiple-choice section. The exam is a live, scoped environment with a time limit, and the deliverable is the same professional pentest report a client would receive.
Live environment
Client-grade report
Voucher included
Every lab is defined as Infrastructure-as-Code under the hood. You never need to touch Terraform yourself. One click in the student portal spins up an isolated scenario in your own cloud account, and tears it back down when you are done.
Launch, reset, destroy, and track every lab from a single portal. Built-in cost controls keep cloud spend predictable.
You buy the course once. New modules, labs, and tradecraft appear in your portal as the course grows, at no additional cost.
WKL is veteran-owned, and the instructors still run offensive engagements for clients. The material is written from that chair.
A dedicated module on the professional-judgement moments every working pentester eventually faces. Production outages caused by your scanner, access lockouts mid-engagement, mid-test scope changes, and existing compromise discovered on the client network. Knowing how to handle these is the difference between a junior who panics and one who keeps getting booked.
Production outage
Credential lockout
Scope-change requests
Existing compromise found
One voucher ships with the course. Sit the exam next month, next year, whenever you are ready for it.
Live help from instructors, hint channels, lab discussion, and alumni. Somewhere to go when you are stuck for more than a few minutes.
External, internal, Active Directory, web, API, cloud, container, client-side, phishing, and physical vectors. If a real engagement is likely to touch it, we cover it.
External
Internal
Active Directory
Web & API
Cloud
Phishing
Client-side
Physical
ELPT covers every domain a working pentester tends to touch during their first year on the job, with hands-on labs across all of them rather than a quick tour of each.
TCP/IP, Linux and Windows internals, pentester tooling, traffic analysis, and lab operations through the student portal in your own cloud account.
Passive and active recon, DNS, subdomain enumeration, service discovery, attack-surface mapping, and prioritising initial access vectors.
Internal enumeration, SMB, LDAP, and MSSQL abuse, tunnelling across segmented networks, and SOCKS and SSH forwarding techniques.
Classical AD attacks including Kerberoasting, AS-REP roasting, ACL abuse, delegation attacks, and DCSync, plus modern tradecraft.
OWASP Top 10 in context: auth bypass, IDOR, SSRF, deserialization, SSTI, and API-specific vulnerability chains.
AWS, Azure, and GCP attack paths, IAM abuse, metadata service attacks, exposed secrets, container escapes, and CI/CD pipeline compromise.
Payload crafting, phishing operations, physical access vectors, and the social engineering reality of modern engagements.
Light AV and EDR evasion, egress awareness, constrained-environment tradecraft, and tuning payloads when the easy path fails.
Windows and Linux privilege escalation checklists, credential dumping, persistence awareness, and impact validation.
Our “When Things Go Wrong” module. Scenario-based exercises on handling production outages caused by your testing.
Executive summaries, technical findings, risk ratings, remediation guidance, and the deliverables clients actually read.
A full external-to-domain-admin scenario that stitches every skill together into one engagement before you sit the exam.
The ELPT curriculum is sequenced the way a real engagement unfolds — foundations, external, internal, Active Directory, web, cloud, client-side, and reporting. Every module ships with hands-on labs you launch from the portal.
What a working pentester does, module by module.
The full, up-to-date module list is pulled live from the WKL Student Portal so this page always matches what’s inside the course. If you’re seeing this placeholder, the API call is pending wire-up.
ELPT does not run on shared lab pods. Every lab is defined as Infrastructure-as-Code under the hood, but you do all of the work from the student portal. One click stands up an isolated scenario inside your own cloud account, and another click tears it back down. You attack it, you break it, you rebuild it if you need to, and you move on when you are done.
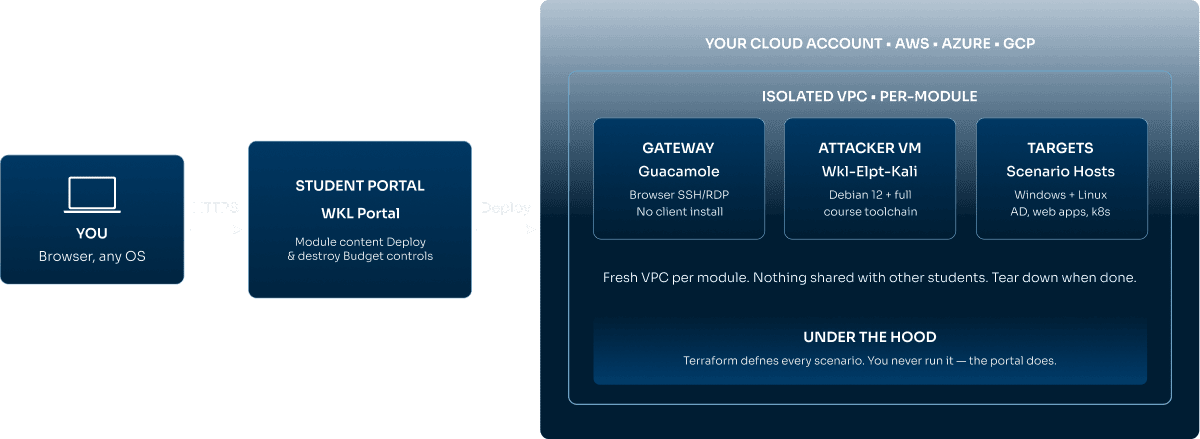
The private lab stacks run in your own cloud account, which gives you full access and full control without any shared state between students.
Lab deployment is handled by the portal, so you never have to write or run Terraform yourself. The infrastructure-as-code lives behind the deploy button, which keeps setup simple and reproducible.
You deploy a scenario, run the lab, and destroy it when you are finished. Cost controls are built into the portal so you can keep an eye on spend.
The labs are modeled on real-world engagement patterns, including misconfigured Active Directory, cloud IAM traps, segmented networks, and reasonably hardened endpoints.
If you get stuck on a lab, you can tear it down and start it again. Lifetime course access means you can keep doing that for as long as you need to.
You will need accounts in all three clouds for the full course. Most labs run on AWS, and specific modules use Azure or GCP where that cloud is the better fit for the attack path being taught.
Study the objective, scenario, and methodology.
Launch the lab or receive scenario credentials through guided controls.
Map hosts, services, users, apps, and exposed attack surface.
Validate findings, gain access, escalate, and demonstrate impact.
Capture evidence and document risk like a real engagement.
Rebuild or destroy labs on demand and keep practicing.
There are no multiple-choice questions on the ELPT exam. You are given a live network, a scope document, and a time limit, and the task is to enumerate the environment, gain a foothold, escalate from there, and demonstrate real business impact. Once the technical portion is over, you write up what you did in a professional report, the same way you would at the end of a real engagement.
You get 48 hours on the network itself, followed by another 48 hours to produce the report. One exam voucher is included with the course, and it does not expire, so you can sit the exam whenever you feel ready for it.
The included voucher is one attempt. If you do not pass, you can purchase another attempt separately. Your course access and labs stay with you, so there is no extra cost to prepare for a resit.
Download a redacted sample ELPT exam report so you know exactly the deliverable quality you are being asked to produce. Executive summary, scoped findings, risk ratings, reproduction steps, and remediation guidance, in the same format a working pentester hands to a real client.
20 pages
Redacted sample
You do not need any prior penetration testing experience. ELPT is aimed at people who are starting out and want a credential, plus a sample report in their portfolio, that actually helps them land interviews.
What moves a hiring manager is proof you can do the work. ELPT hands them a real report you wrote against a live network, not just a line on a resume.
When you pass the exam, you earn the White Knight Labs Entry-Level Penetration Tester certification. Because the credential is tied to a report you actually wrote on a network you actually broke into, it tends to carry more weight with people who read a lot of resumes.

ELPT is a new certification. The people behind it are not. It was built by a team of White Knight Labs operators, each a specialist in their own area, at a veteran-owned firm that runs real red team and penetration testing engagements for clients. Every module is written and maintained by someone who does that work for a living.
You do not pass by answering questions. You break into a live network and write the report, so the credential is backed by work a hiring manager can actually read.
The course is built, maintained, and graded by a working offensive security firm, not a content mill. The labs and exam reflect how engagements actually run.
Every certificate carries a unique ID and a verification URL, so an employer can confirm it in seconds.
ELPT is early in its life. Certifying now puts you in the first group to hold it as recognition grows, with a real report in your portfolio from day one.
ELPT · WKL Certification
Course code
ELPT
Track
WKL Certification
Difficulty
Beginner-Friendly
Delivery
On-Demand / Self-Paced
Modules
24+ with 100+ labs
Estimated effort
120–180 hours
Language
English
Course access
Lifetime (portal)
Content updates
Included for life
Lab platform
Deployed from the student portal
Supported clouds
AWS, Azure, GCP (AWS primary)
Cloud accounts needed
All three
Cloud account
Student-provided
Lab reset
Unlimited
Support
Discord community + email
Enrollment
Open / on-demand
Format
Performance-based, live environment
Technical window
48 hours
Report window
48 hours
Deliverable
Professional pentest report
Exam voucher
One included · never expires
Retakes
Additional attempt purchased separately
Retakes
Reduced-price voucher available
Proctoring
Remote, scheduled on your time
Official ELPT certification
Validity
Never expires
Verification
Public URL + unique cert ID
Digital badge
LinkedIn-ready
Eight things most entry-level pentest certifications do not give you in one program.
You pay once. New modules, lab refreshes, and tradecraft updates stay yours as the course evolves. One exam voucher is included and does not expire.
No multiple-choice questions. You enumerate, exploit, and demonstrate business impact against a real environment, then write it up the way you would at the end of a client engagement.
Every scenario stands up inside its own VPC in your own cloud account. No queues, no timers, no state shared with other students. Rebuild, break, repeat for as long as you own the course.
Modern Active Directory on Server 2025, AI and LLM pentesting, containers and CI/CD, and the vulnerability classes active pentesters use on real engagements. Content was last reviewed and updated in 2026.
A dedicated cloud module across all three major providers: identity abuse, metadata-service exploitation, service-account escalation, exposed storage, and cross-cloud credential discovery against CIS Benchmarks.
Kerberoasting, AS-REP, ACL abuse, and DCSync, taught alongside Active Directory Certificate Services misconfigurations, Shadow Credentials, Resource-Based Constrained Delegation, and dMSA abuse on Server 2025.
Production outages caused by your scanner, credential lockouts, mid-engagement scope changes, and finding existing compromise on the client network. A full module on the professional-judgement moments every working pentester faces and most courses skip.
Four specialized modules included in the base course, not sold as separate certifications. The attack surfaces real pentesters meet in their first year that an eight-week cert cannot fit alongside the basics.
A side-by-side on the things that change your outcome, not the logo on the certificate.
| Feature | ELPT | Typical Entry Cert |
|---|---|---|
| Exam Format | Live Network, 48 Hours, Then A Report |
Flags Or Multiple Choice |
| Professional Report | Required, Client-Grade Deliverable |
Rarely Required |
| Course Access | Lifetime |
3 To 12 Months |
| Content Updates | Free For Life |
Pay For The New Version |
| Labs | Private, In Your Own Cloud |
Shared VPN Pods |
| Specialized Tracks | Cloud, AD, AI/LLM, Wireless, Thick Client |
Sold Separately Or Not Covered |
| Exam Voucher | Included, Never Expires |
Often Separate Or Time-Limited |
| Price Model | Pay Once |
Often Separate Or Time-Limited |
Yes. ELPT is designed for people who are new to penetration testing. The course opens with foundational material (networking, Linux, Windows, and lab operations) and gradually works up to a full external-to-domain-admin engagement, so you do not need prior pentesting experience to get started.
ELPT is built to prepare an entry-level pentester for a working junior role, not to pass a quiz. The curriculum covers current cloud attack paths across AWS, Azure, and GCP, classical and modern Active Directory on Server 2025, modern application attack surface including APIs and token abuse, specialized tracks for thick client, wireless, AI and LLM pentesting, containers, and CI/CD, phishing operations, and the professional-judgement moments on real engagements. The labs run inside your own cloud account rather than a shared pod, deployed from the student portal with a single click, so there is no queue or wait list. The exam is a short consulting engagement with a professional report, not multiple choice. Course access and updates are included for life, and the exam voucher does not expire, so there is no deadline pressure to sit the exam before you are ready. The intent is simple: if you finish ELPT and pass the exam, you are ready to walk into a junior pentester role.
There is not a preview of ELPT itself, but White Knight Labs offers free Academy courses that run on the same student portal that hosts ELPT. You can create a free account at studentportal.whiteknightlabs.com/signup, work through one of those free courses, and see how the portal, content, and lab deployment feel before you commit to the full certification.
No prior pentesting experience is required. Some basic TCP/IP, Linux and Windows familiarity, and comfort with the command line will make the first few modules easier, but every concept is taught from the ground up.
The course is fully self-paced and on-demand. You keep access for life, work at whatever tempo suits you, and have live support through the WKL Discord when you get stuck.
Real pentests happen inside real cloud environments, so lab deployment goes into your own accounts rather than a shared pod. You will need an AWS, Azure, and GCP account for the full course. Most labs run on AWS and a few modules use Azure or GCP. The portal handles the deployment itself, so you do not need to know Terraform or infrastructure code to run a lab. You should expect some cloud spend per lab session rather than running labs entirely for free, and the portal offers one-click teardown so costs stay predictable once you set a cloud budget on your side.
Anything that runs a modern browser. The attacker workstation and lab environments live inside your cloud account and you reach them through the student portal, so there are no local RAM, CPU, or GPU minimums. A current Mac, Windows, or Linux laptop with a reliable internet connection is enough to complete the course.
Lab spend is small if you manage it. Most students run around $20 per month or less when they tear labs down after each session and set a cloud budget to catch runaway resources. AWS, Azure, and GCP each expose their own billing alerts and budget caps, and configuring those on your side before you launch your first lab is the single most important thing you can do to keep spend predictable.
The exam is modeled on a short consulting engagement rather than a quiz. You get 48 hours inside a live multi-host environment, followed by another 48 hours to deliver a professional pentest report. Scoring is based on technical execution, evidence quality, and the clarity of the write-up, which are the same three things actual clients pay for. One exam voucher is included and it never expires. It covers one attempt, and if you do not pass you can purchase another attempt separately.
You can purchase a reduced-price retake voucher. The course materials and labs are yours for life, so you can go back, close whatever gap tripped you up, and sit the exam again when you are ready.
No. The ELPT exam is not proctored. We do not use screen recording, webcams, or any form of remote monitoring. The exam is graded on your technical execution against a live network and the professional report you deliver, which are difficult to fake. Working on your own terms with normal access to your notes and references mirrors the conditions of a real client engagement, which is what the exam measures.
Yes, in depth. Classical AD is covered first: enumeration, Kerberoasting, AS-REP roasting, ACL abuse, lateral movement, and DCSync. A dedicated companion module then teaches the modern AD attack catalogue: Active Directory Certificate Services misconfigurations (ESC1, ESC13, ESC15), Shadow Credentials via msDS-KeyCredentialLink, Resource-Based Constrained Delegation, dMSA abuse on Server 2025, writable GPO exploitation, and LAPS and gMSA read-right findings. The two modules together give an entry-level pentester the full AD toolkit they will meet on real engagements.
Yes. A dedicated Cloud Security Fundamentals module covers AWS, Azure, and GCP end to end, including IAM policy abuse, EC2 metadata service exploitation via SSRF, over-permissioned Entra ID app registrations, GCP default service account escalation, public cloud storage exposure, and cross-cloud credential discovery against CIS Benchmarks. Containers, Kubernetes, and CI/CD attack paths get their own module. Modern application attack surface, including REST APIs, GraphQL, JWT, and OAuth, is covered in the web module. Phishing, client-side payload delivery, and physical-security awareness are a separate module in the course.
It is a dedicated incident-response and professional-judgement module. Every working pentester eventually faces a production service that crashed under their scanner, a credential lockout at 16:45 on a Friday, a mid-engagement scope expansion request across jurisdictions, evidence that someone else has already compromised the client’s network, or something on a file share that suggests illegal activity by a client employee. The module works through those exact scenarios with incident-communication drafts, escalation workflows, and the three principles that come up every time: communicate early, communicate honestly, document everything. No tools to install, no target hosts, just the exercises that separate a junior who panics from one who handles it.
Most students complete the course and sit the exam within 3 to 6 months at a part-time pace. Total content works out to roughly 120 to 180 hours of lab time, depending on how deeply you dig into optional material.
Course access does not expire. All future content updates land in your portal at no additional cost, so you keep an up-to-date version of the course for life.
All ELPT purchases are final. You receive immediate access to the full course, every lab, and the exam voucher at the moment of purchase, so we do not offer refunds. If you have questions about the course scope before you buy, reach out through our contact channels and we are happy to answer them.
No. The ELPT credential does not expire. Once you pass the exam, you hold the certification without a renewal fee or a continuing-education requirement.
Not at this time. ELPT does not currently grant formal CPE or CEU credits toward other certifications such as CISSP or CompTIA. Many students use the course and exam preparation hours to satisfy self-reported CPE requirements where their certifying body allows it, but we do not provide an official CPE partnership.
Help is available through the White Knight Labs community Discord, where instructors, alumni, and other students stay active, and by email at support@whiteknightlabs.com.
Yes. We offer team and enterprise licensing with volume pricing, usage reporting, and optional instructor-led kick-off sessions. Please reach out at info@whiteknightlabs.com for details.
The course is only available in English at this time.
Enroll today and you can launch your first lab tonight. Your exam voucher never expires, course access is for life, and so are the content updates, so there is no pressure to rush through the material before you are ready.
Full course · 24+ modules · 100+ labs · exam voucher that never expires · lifetime access & updates
Most entry-level certs bill again every year, or charge for every exam retake. ELPT is one payment. Over three years, paying once usually costs less than the renew-and-retake path.
Beginner-Friendly · Performance-Based Exam · Cloud-Native Labs · Lifetime Access · Veteran-Owned
Loading modules...
All seats for this training are currently filled, but you can still get in line for the next available spot. Leave your details below, and we’ll notify you as soon as a place becomes available.